News
Closing the gap: How digital forensics and intelligence can work smarter together
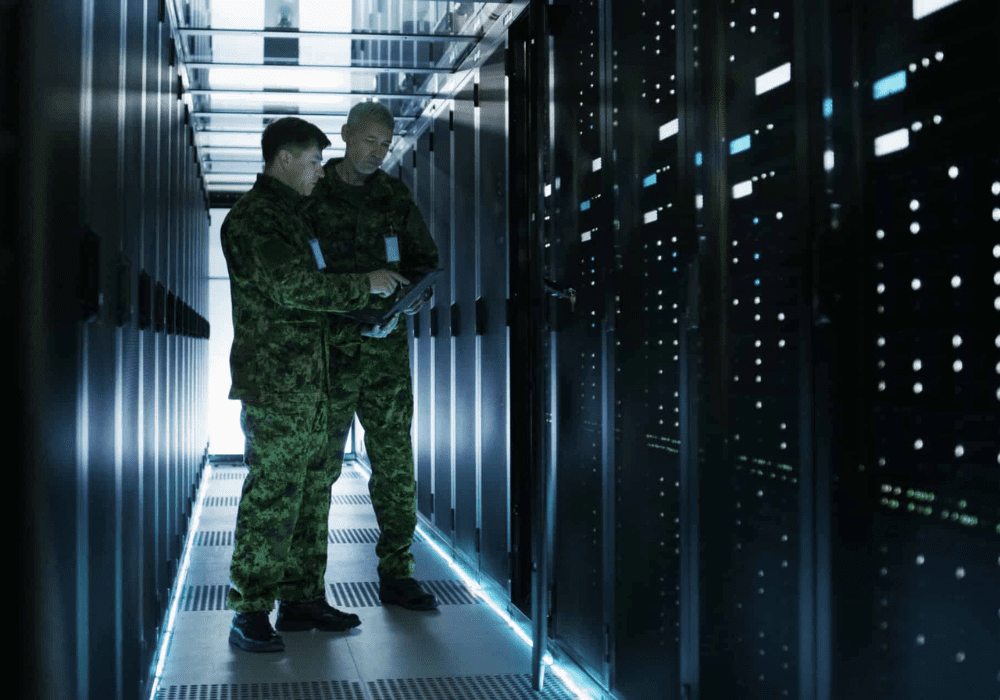
In today's research, one thing is certain: data is everywhere. Every seized phone, laptop or cloud account holds a potential trove of information. While digital forensics teams work tirelessly to extract and analyze that data for the courts, intelligence units are often just meters away, building operational pictures and identifying threats.
The problem? These two worlds don't always overlap as much as they should.
Lost opportunities?
Digital forensics departments are maximally focused on evidentiary integrity, gathering evidence that will stand up to trial. That work is essential, but it can mean that valuable patterns, associations and leads remain locked in files long after they could have made an operational difference.
Meanwhile, intelligence units—in areas such as serious and organized crime, counterterrorism, and child sexual exploitation and abuse—must detect risks early, map networks, and direct resources. Without timely and adequate access to the full scope of forensic data, they may be making decisions without the clearest picture possible.
Why it happens
-
Different priorities:digital forensics teams build evidence packages; intelligence people chase clues.
-
Data silos:Security protocols and legal boundaries can restrict what each side sees.
-
Specialized tools:Many forensic tools require training and expertise that intelligence teams do not have.
It is not about lack of will; These are workflows, access models, and technology that still fall short of the need for secure, compliant collaboration.
What good focus looks like
Imagine an ecosystem of digital evidence and intelligence: a connected workflow where both digital forensics and intelligence work on the same basis, respecting legal and procedural safeguards.
In this approach:
-
Intelligence teams can securely access and review relevant digital evidence from forensic extractions without compromising thechain of custody.
-
Forensic experts can focus their efforts with a richer operational context provided by intelligence.
-
Access is covered by strict controls and protocols: only authorized personnel view relevant material, and all activity is recorded and auditable.
-
Legislative and procedural compliance is incorporated, so as not to jeopardize the admissibility of the evidence.
-
Advanced tools can map associations between people, objects, places and events (POLE), bringing to light connections that would otherwise go unnoticed.
-
Operational practices can be shared between departments, identifying targets that could appear in multiple crime typologies.
The result? Cases move faster, evidence is stronger, and resources are used more efficiently, all without breaking legal or ethical boundaries.
Bringing vision to reality…
It's not a fantasy. Solutions likeMagnet ReviewThey are already helping to close the gap by providing non-technical users – such as intelligence officers and investigators – with controlled, role-based access to digital evidence. Without requiring digital forensic training, they can search, review and identify key material that guides the direction of an investigation.
Combined with tools likeGriffeye EnterpriseFor powerful POLE (people, objects, places, and events) analysis, agencies can begin to break down silos while maintaining data integrity, security, and admissibility.
The multiplier effect
When digital forensics and intelligence workflows connect securely and compliantly:
-
Clues are detected earlier.
-
Reduces duplication, freeing up researchers' time.
-
Identification of offenders is accelerated, crucial in time-sensitive cases.
-
Improves protection, since victims are identified and protected sooner.
It's not just about sharing data. It's about working smartertogether, without ever compromising the integrity of the investigation. And in a world where the volume of digital evidence only goes in one direction, that kind of collaboration is no longer optional: it's essential.